HTTPS proxy
An HTTPS proxy is a proxy you connect to over an encrypted (TLS) link, so even the name of the site you ask it for is hidden from your local network.
Explanation
In depth
The term is used two ways. Strictly, an HTTPS proxy is one your browser reaches over TLS: the CONNECT request that names your destination travels inside encryption, so your network sees only that you talked to the proxy. With an ordinary HTTP proxy, that request is readable on your network. Loosely, people say HTTPS proxy for any proxy that can carry https:// sites, which today is nearly all of them. What matters more than the name is what happens to the encryption. A tunnelling proxy passes your browser's own TLS session through untouched, so only you and the site hold the keys. A web proxy works differently: there are two separate encrypted connections, one from your browser to the proxy and a second one the proxy opens to the site. The proxy decrypts in between so it can rewrite the page. AnyProxy works this way, and its privacy policy says so plainly. Your network sees anyproxy.site; the network between the proxy and the site sees the proxy's own handshake.
In practice
HTTPS proxy in the real world
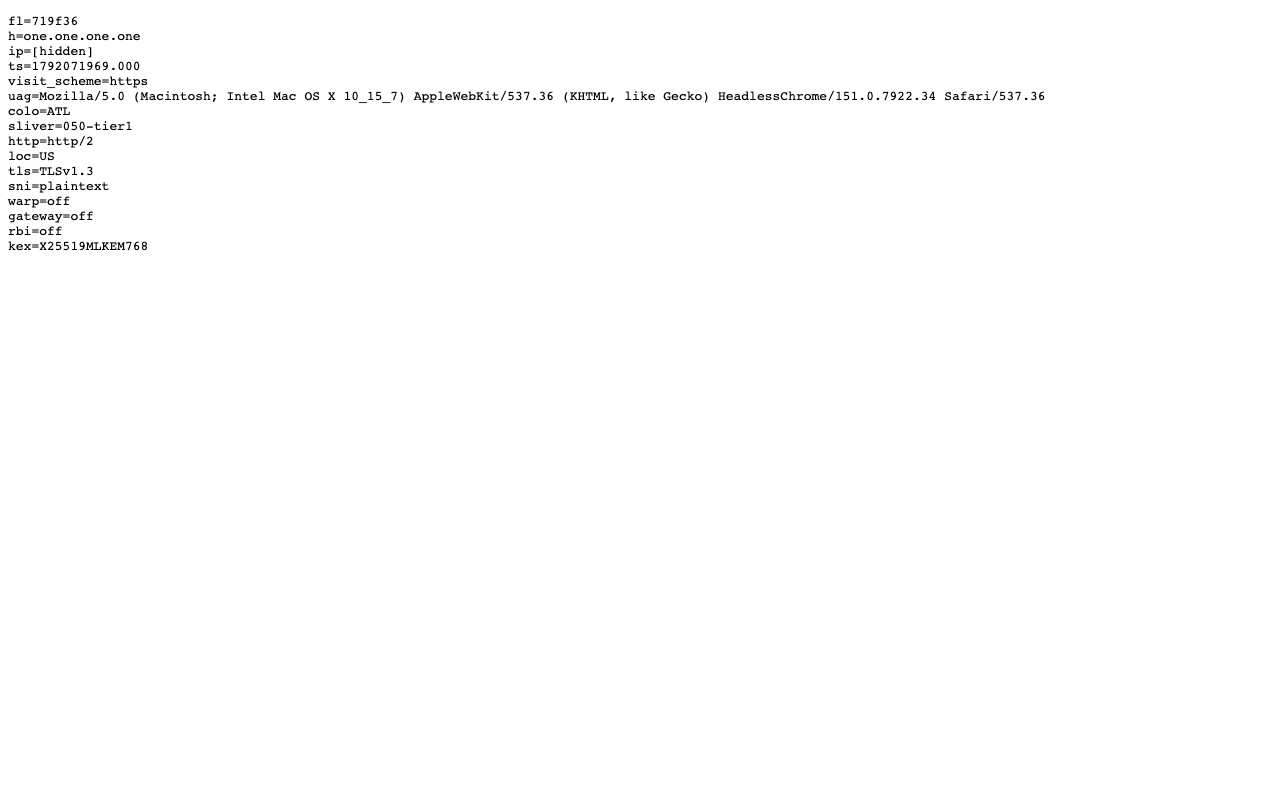
You can watch the second encrypted connection. On 15 October 2026 we opened Cloudflare's trace page through AnyProxy's Virginia server. Cloudflare described the connection it received, which was the proxy's, not the browser's: tls=TLSv1.3, http=http/2, kex=X25519MLKEM768 (a post-quantum hybrid key exchange) and sni=plaintext, meaning the site name was readable in that handshake. loc=US and colo=ATL placed it in the United States. None of this is visible to your own network, which only sees a TLS connection to anyproxy.site.
Sources: Cloudflare trace page used in the test · AnyProxy privacy policy
We checked
The proxy's own TLS connection, as the site saw it
Questions about HTTPS proxy
Related terms